AHP-TOPSIS-Based Cybersecurity Control Prioritization for Local E-Government: Integrating COBIT 2019 and ISO/IEC 27001:2022 in Ecuador
DOI:
https://doi.org/10.5281/zenodo.22825222Keywords:
cybersecurity governance, AHP-TOPSIS, COBIT 2019, ISO 27001, local e-government, MCDM, EGSI EcuadorAbstract
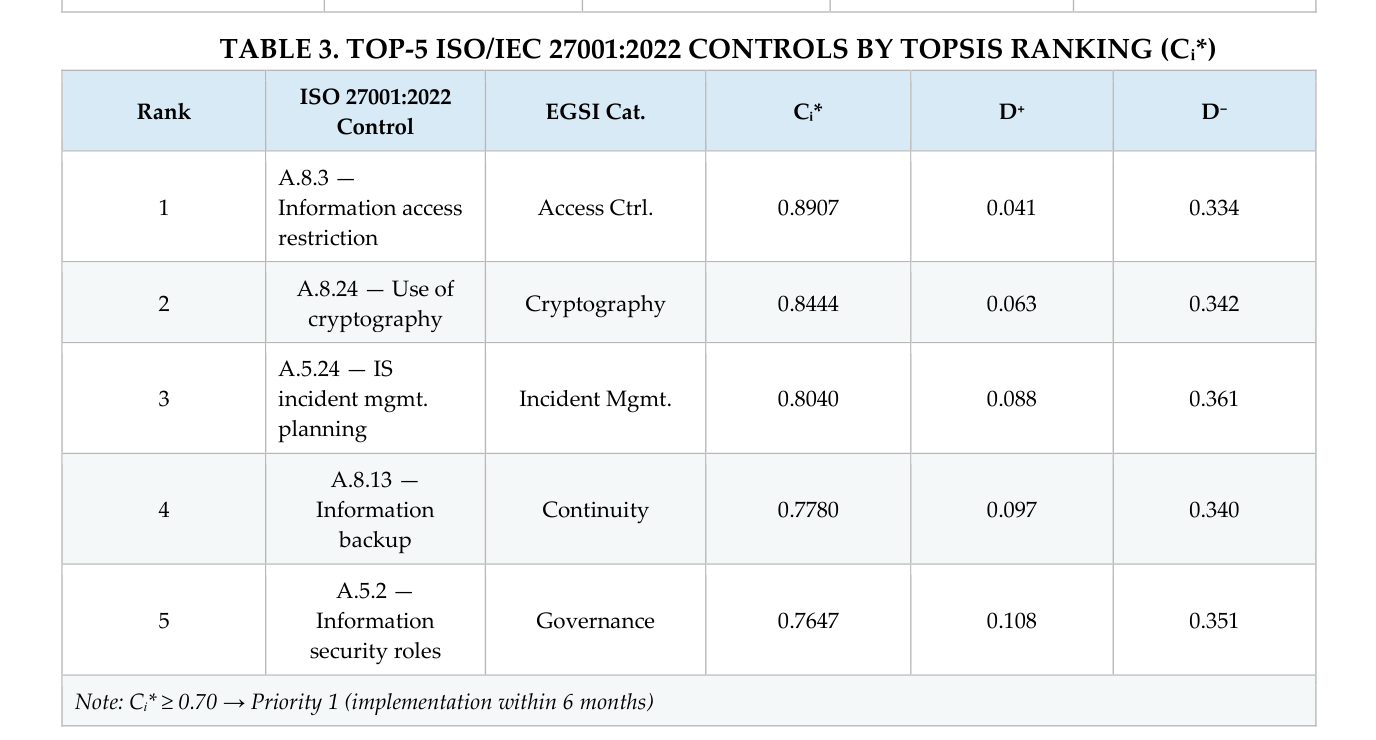
Local governments in Ecuador manage critical citizen services yet operate with limited cybersecurity maturity. This paper presents MPEC-GAD, a cybersecurity governance model integrating COBIT 2019 strategic alignment with ISO/IEC 27001:2022 technical controls, using AHP-TOPSIS multi-criteria prioritization. Applied to GAD Jaramijó (Manabí, Ecuador), the model uses a reported baseline MIL of 1.0 and treats 2.8 within 36 months as a planning target, not an observed outcome (+1.8 points). The four decision criteria weight risk reduction at 48.24%, implementation cost at 27.18%, deployment time at 15.75%, and technical complexity at 8.83% (AHP Consistency Ratio CR = 0.0054 < 0.10). The TOPSIS ranking directs scarce resources toward the 47 mandatory EGSI controls with highest risk-reduction per investment unit. The model addresses LOPDP compliance requirements (up to 3% revenue penalties) and aligns with Ecuador's EGSI v3.0. A single-round structured review by seven experts rated pertinence, viability and completeness with mean scores ≥4.0/5.0.
Downloads
Downloads
Published
Versions
- 2026-09-19 (2)
- 2026-09-18 (1)
Issue
Section
License
Copyright (c) 2026 Neutrosophic Sets and Systems

This work is licensed under a Creative Commons Attribution 4.0 International License.